Plenty of organisations can say, with confidence, that everyone has completed their UK GDPR training. Fewer can say what would happen if a real data protection issue landed on someone’s desk tomorrow.
Training can easily become an annual box-ticking exercise: book the session, get people through it, move on. The question is not whether the training happened; it is whether anything proactive regarding personal data processing changed afterwards?
Could Your Team Spot a Data Protection Issue?
Picture these situations:
- An email arrives that might be a Subject Access Request;
- Personal data gets sent to the wrong recipient;
- A new supplier wants access to customer or employee records;
- Marketing wants to reuse existing customer data for a new campaign (new purpose);
- Someone pastes commercially sensitive information into an AI tool;
- A colleague asks for information, and the employee is not sure whether to hand it over.
Nobody needs to know the legal answer on the spot. They need enough awareness to notice that something needs attention, and to know who to ask next.
Why Generic UK GDPR Training Is So Easy to Forget
Abstract explanations of legislation rarely stick, because they are hard to connect to the day job. HR, marketing, senior leadership and customer-facing staff all meet different risks, so training that could have been delivered to any organisation in any sector tends to be forgotten just as quickly as it was delivered. At CSRB, the starting point is making data protection relevant to the people sitting in the room, we want to find out about your organisation and sector.
What Should Good Training Actually Change?
Attendance figures and quiz scores are a poor measure of success. Good training should leave people more confident when handling personal data, allow potential data processing risks to be identified earlier, clarity regarding when to escalate a concern, and be better placed to understand why certain processes exist in the first place and how they can be continually improved. The aim is not to turn every employee into a Data Protection Officer.
Does Everybody Need the Same Training?
Rarely. All-staff awareness sessions, induction training for new starters, sessions aimed at senior leadership and business owners, HR-specific training, and topic sessions on Subject Access Requests, personal data breaches, or direct marketing all serve different purposes. Tailoring training to the audience tends to deliver more than a one-size-fits-all session ever will.
Why Conversation and Real Examples Matter
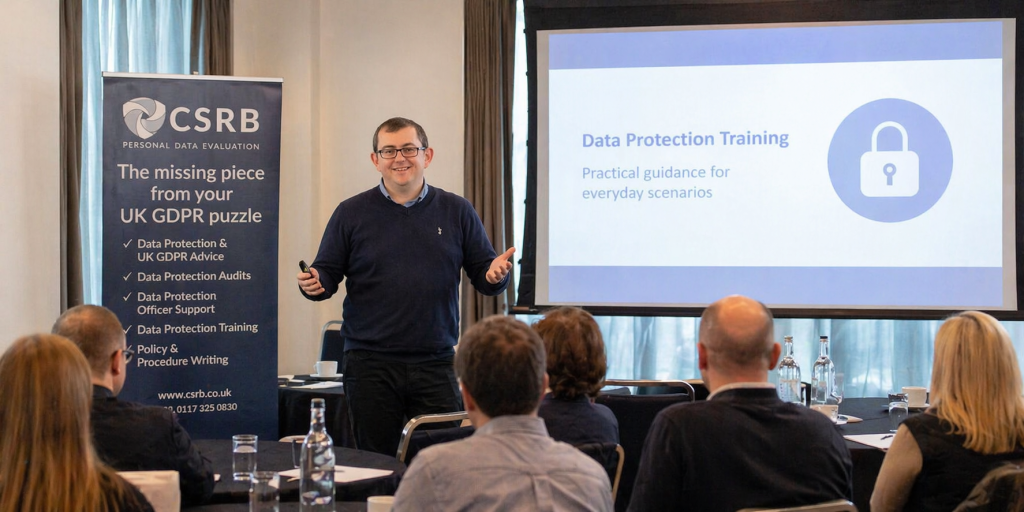
Real scenarios push people to think through how they would respond, and the questions that come up in discussion often reveal gaps that passive training never would. Face-to-face sessions work well where organisations want that back-and-forth, and live online training offers the same tailored approach for remote, hybrid, and dispersed teams. Neither format is second best. CSRB delivers both, with our senior trainer and MD (Chris) based in the Bristol area and well placed to support organisations across the South West in person.
How Often Should Training Be Refreshed?
There is no single correct interval. Staff change, roles change, new systems arrive, new types of personal data get processed, ICO guidance moves on, and people simply forget. Refresher training should respond to that kind of change, rather than being triggered purely by a date in the compliance calendar. Although it is widely accepted that some level of annual refresher training for all roles should be added to your calendar.
The Question To Ask After Your Next Session
Not “has everybody completed their GDPR training?” but “if something involving personal data went wrong tomorrow, would our people recognise it and know what to do next?”
The Real Test Comes After Training Ends
Good data protection training is not about memorising UK data privacy legislation. Employees do not need every answer, only the awareness to recognise when something matters and the confidence to respond or escalate. That value shows up weeks or months later, in a real situation, when better decisions follow.
CSRB provides tailored data protection and UK GDPR training in person across the UK and live online. Contact us to book your no obligation exploratory training requirements session.